Validating Medical Device Cybersecurity Through Penetration Testing: What MDIC's New Best Practices Mean for Developers
June 29, 2026


Premarket cybersecurity documentation for connected devices and SaMD: threat modeling, SBOMs, security risk management and testing evidence.
System architecture views and threat models at the level of detail FDA reviewers look for.
Software bill of materials, vulnerability assessment and support plans for third-party components.
Security risk assessment linked to your safety risk file and design controls.
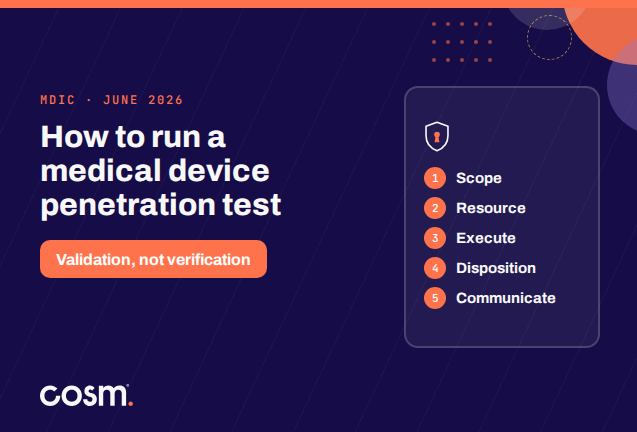
Penetration testing scope, test reports and postmarket vulnerability management plans.